
For journalists, editors and researchers
Data on USDT and TRON, ready to quote.
We process the full USDT TRC-20 transfer stream and keep 65 million labelled TRON addresses. Below are our published findings, the files behind them, and what we can prepare for your story.
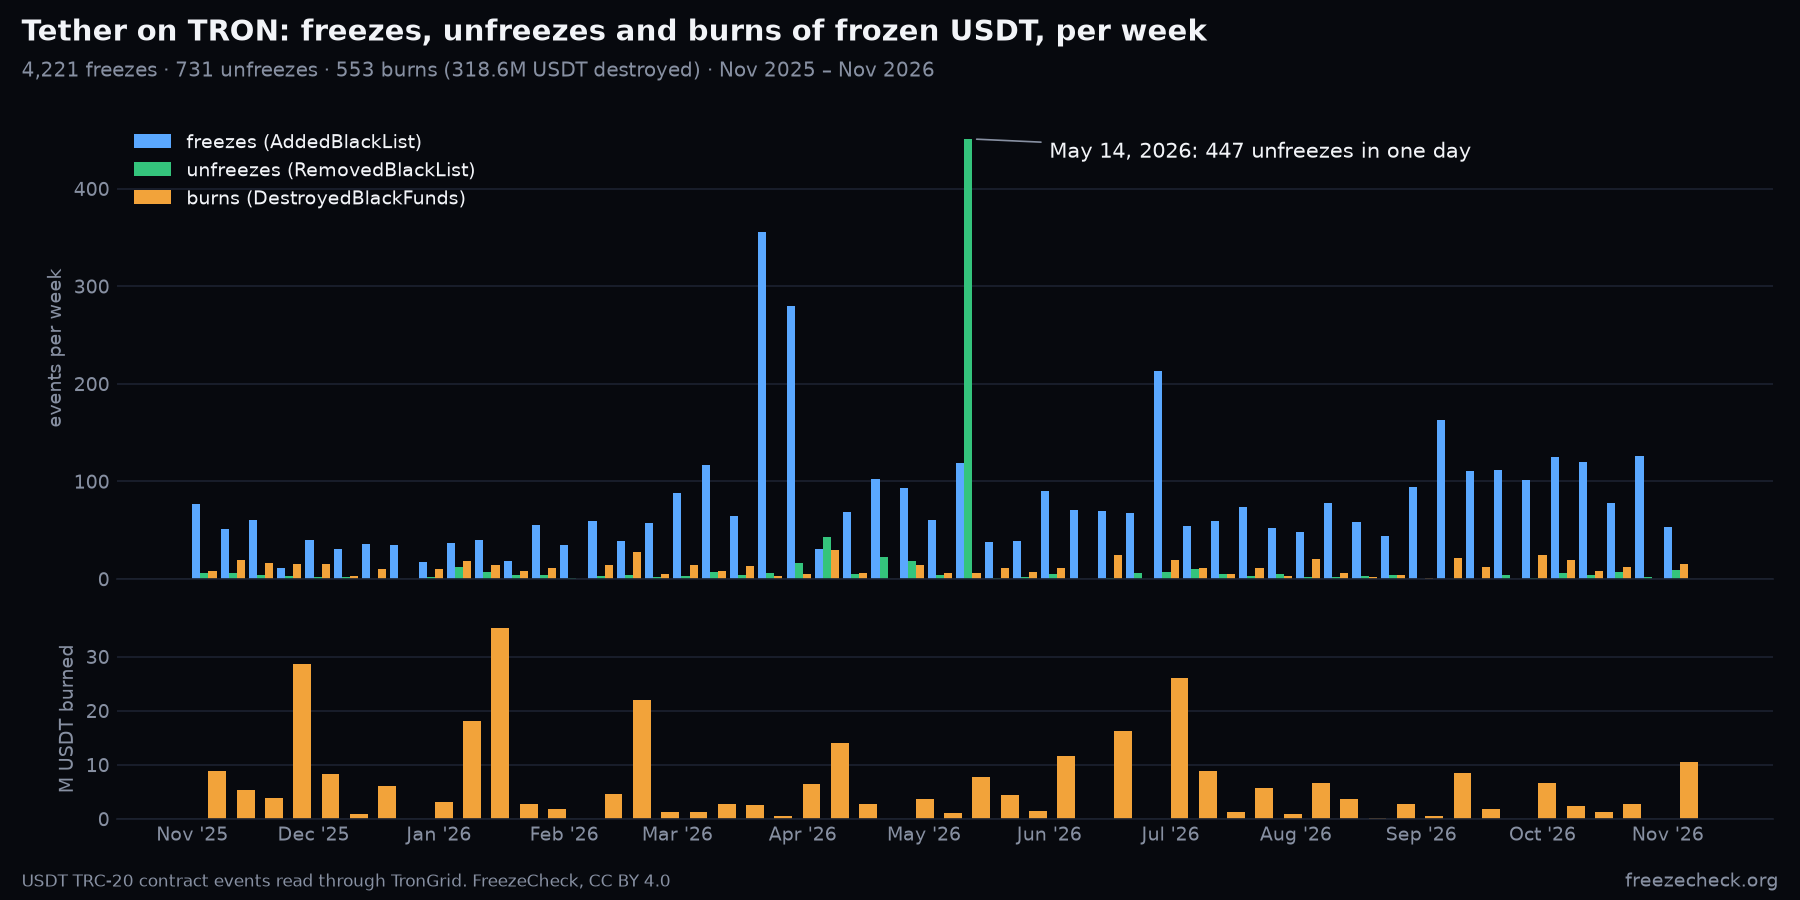
Tether unfroze 731 addresses and burned $318.6M of frozen USDT
447 unfreezes came in one evening, 14 May 2026, all of them addresses frozen in late March. 553 burns destroyed 318.6M USDT held on blacklisted addresses.
Read the study →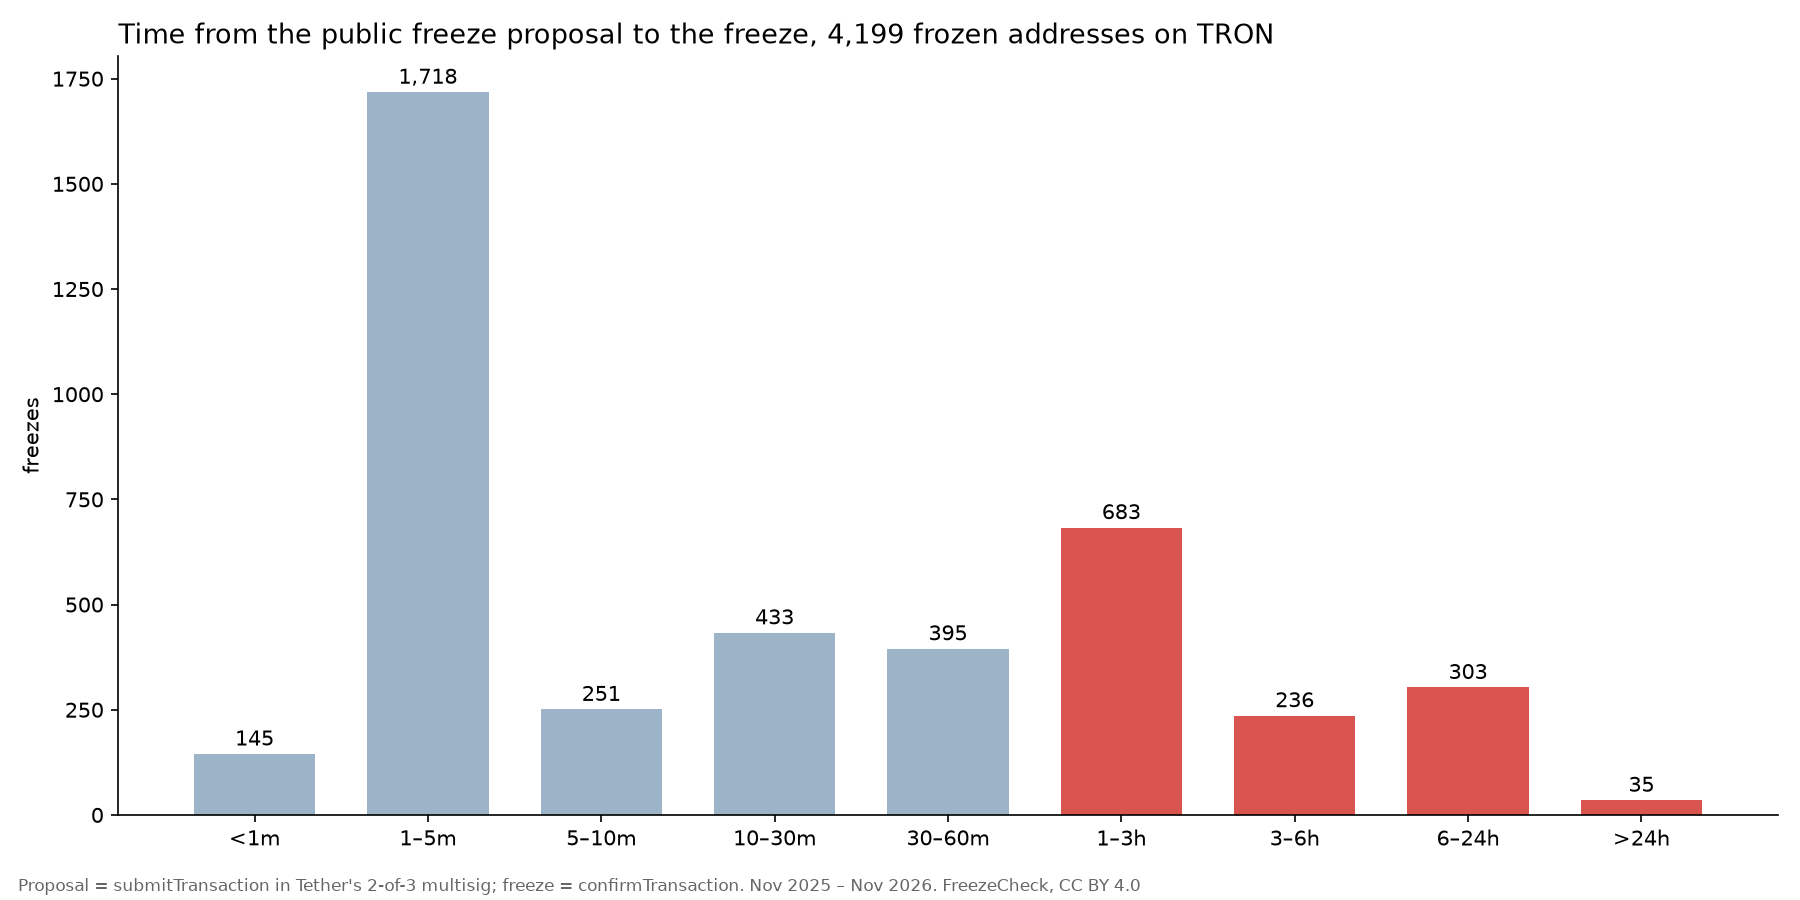
Tether freezes are visible before they happen: $65M left in the window
Each freeze is proposed on-chain in a 2-of-3 multisig first. For 30% of 4,199 freezes the target was public for over an hour. $104M was sent to addresses after they were already frozen.
Read the study →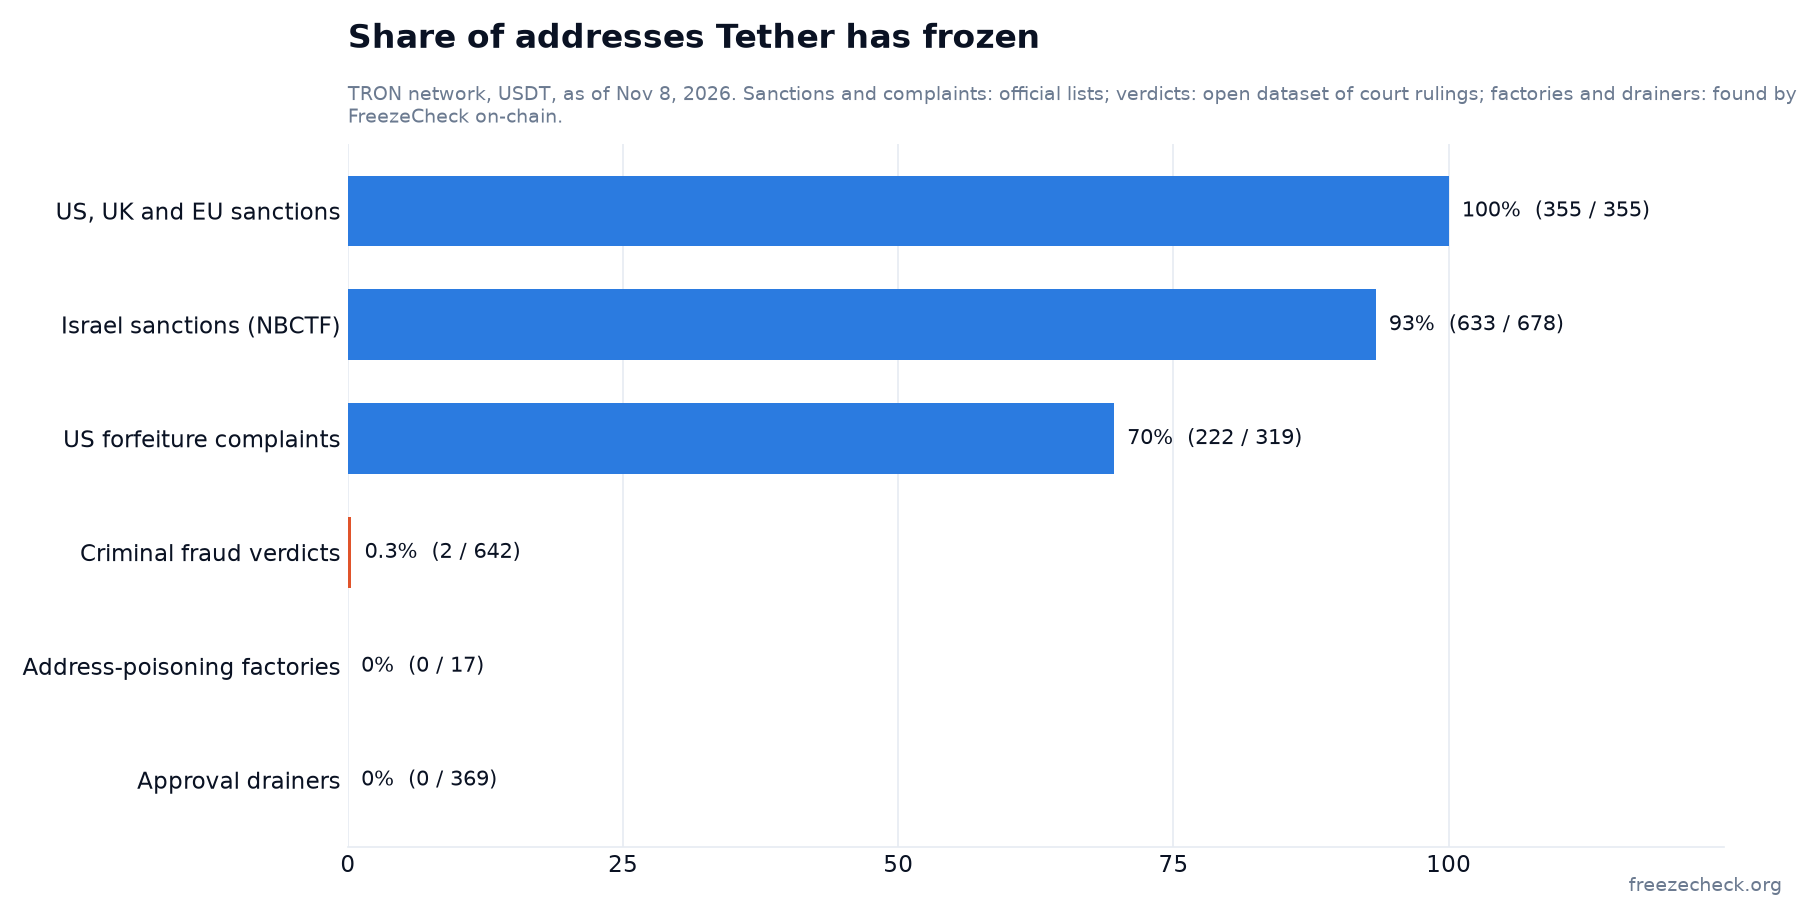
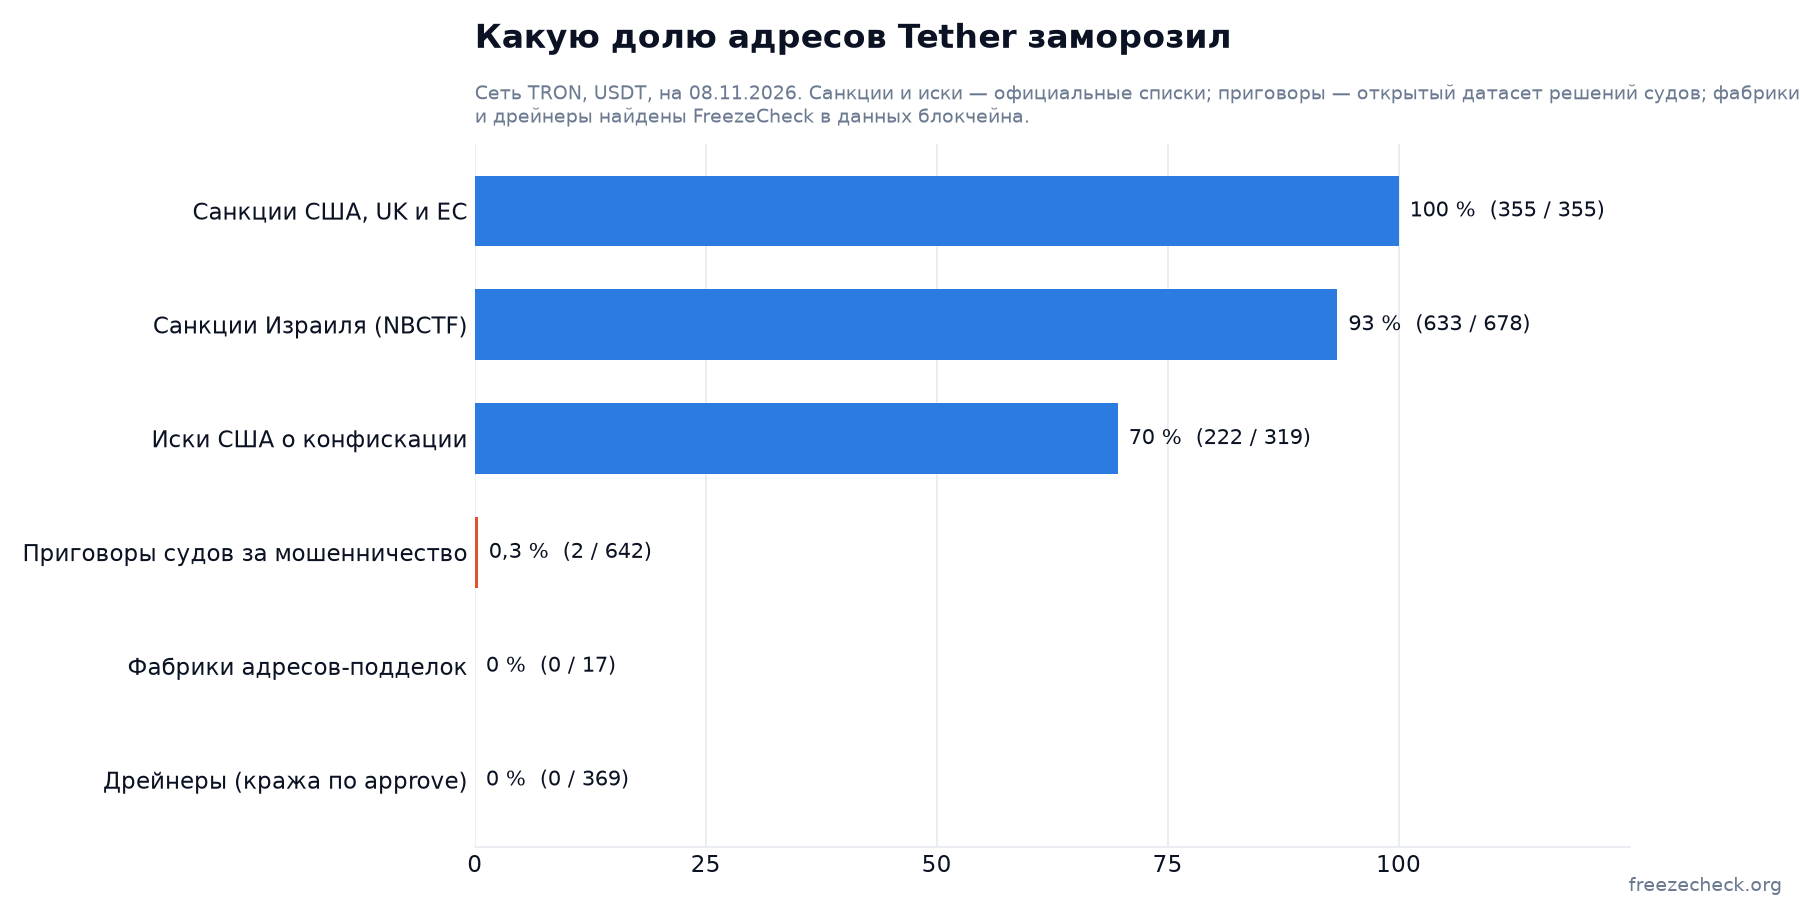
Who Tether freezes: sanctions 355 of 355, drainers 0 of 369
Sanctioned addresses are all frozen, some before the designation was published. Poisoning factories (0 of 17), drainers (0 of 369) and fraud-verdict addresses (2 of 642) still hold 1.25M USDT.
Read the study →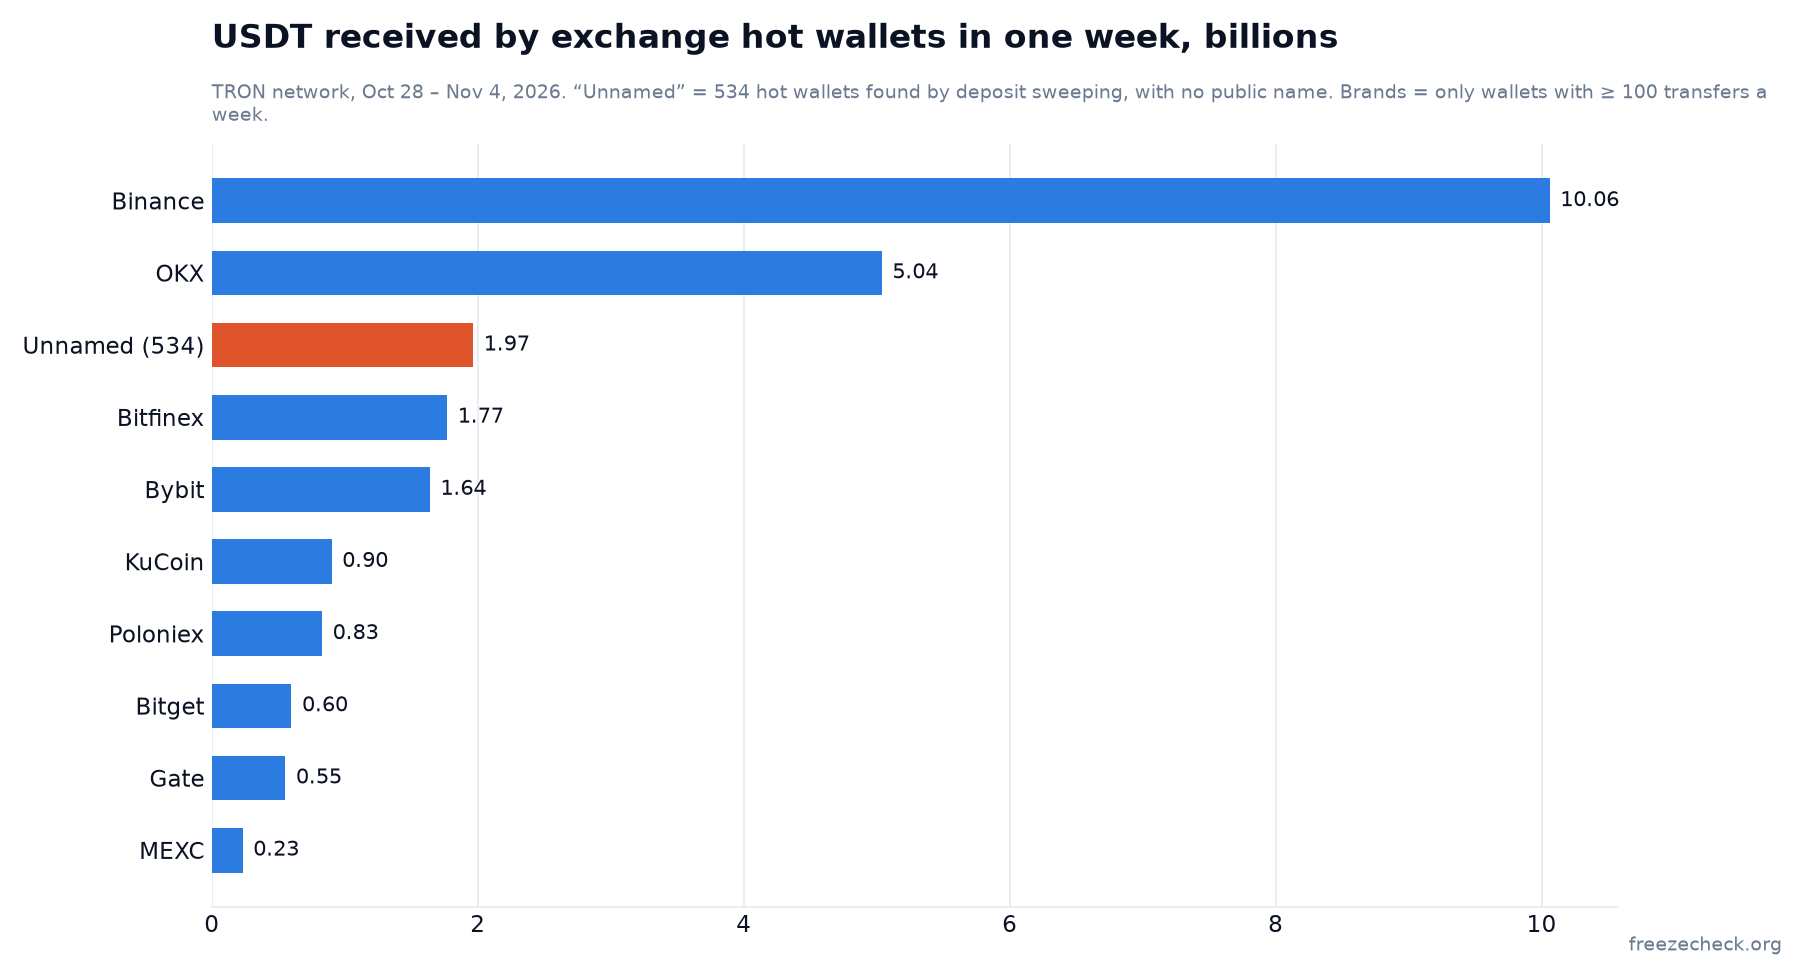
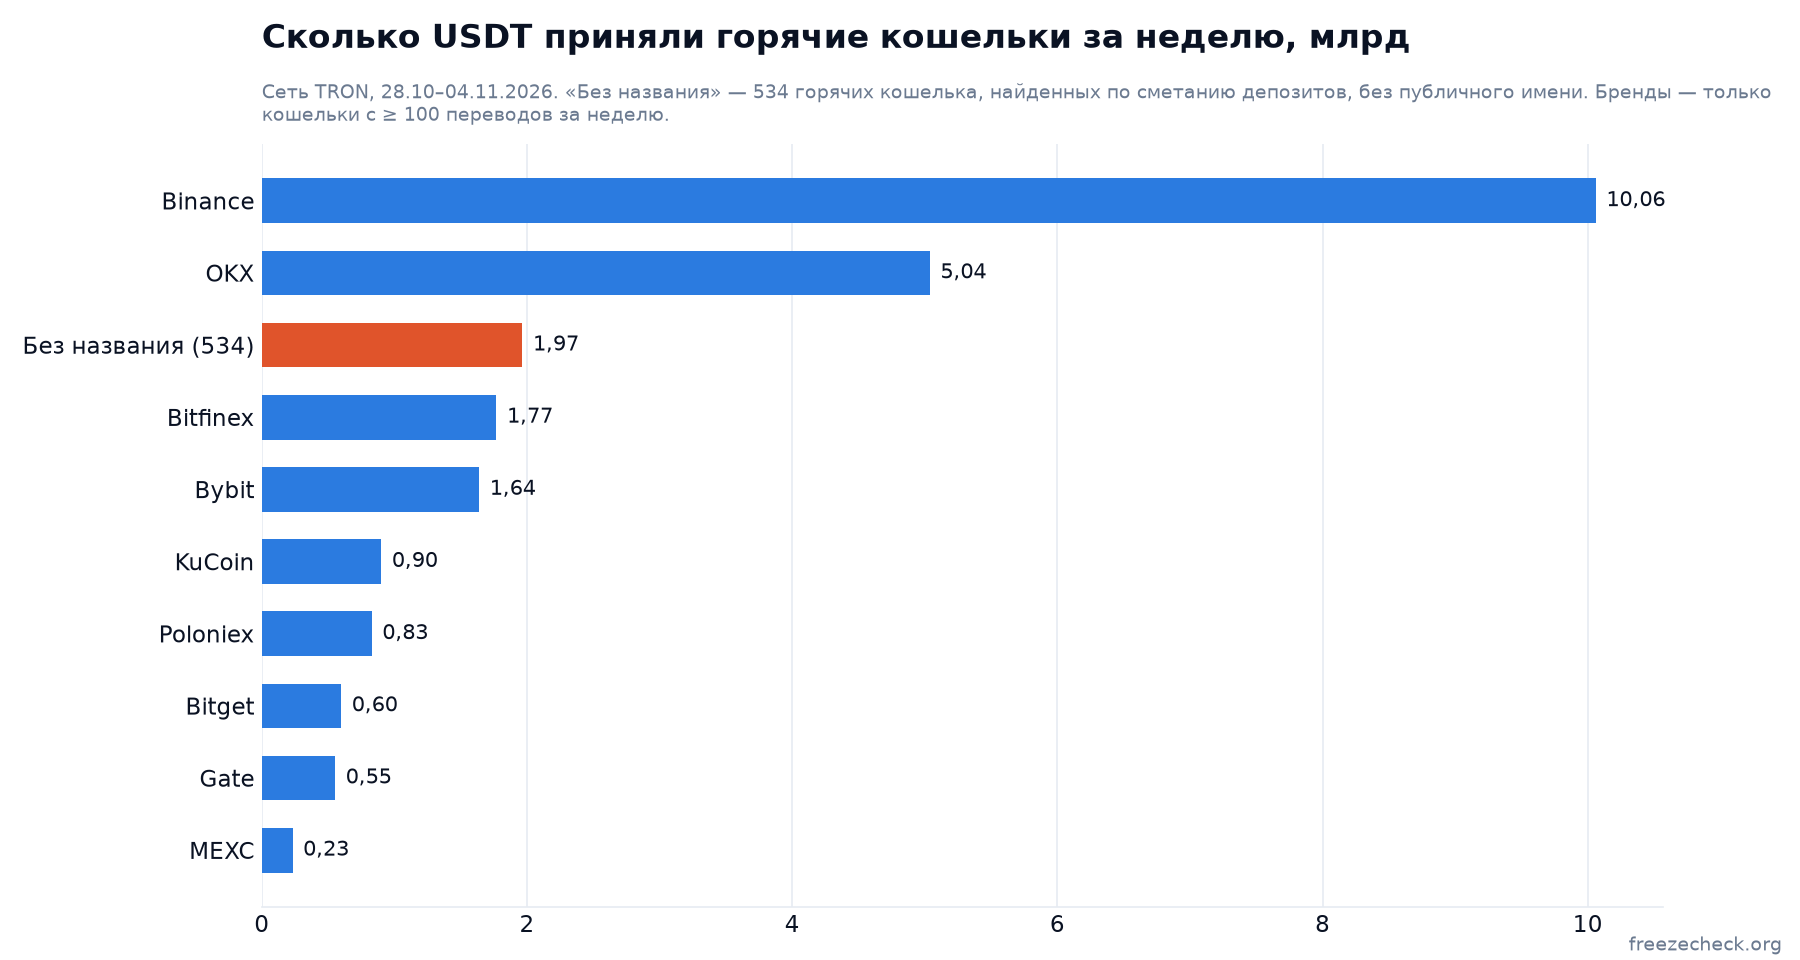
Unnamed exchanges: 534 hot wallets took 1.97B USDT in one week
About 8% of all visible flow into exchange hot wallets, more than Bybit. 260,047 deposit addresses swept into wallets that have no public name; the ten largest have no Tronscan tag.
Read the study →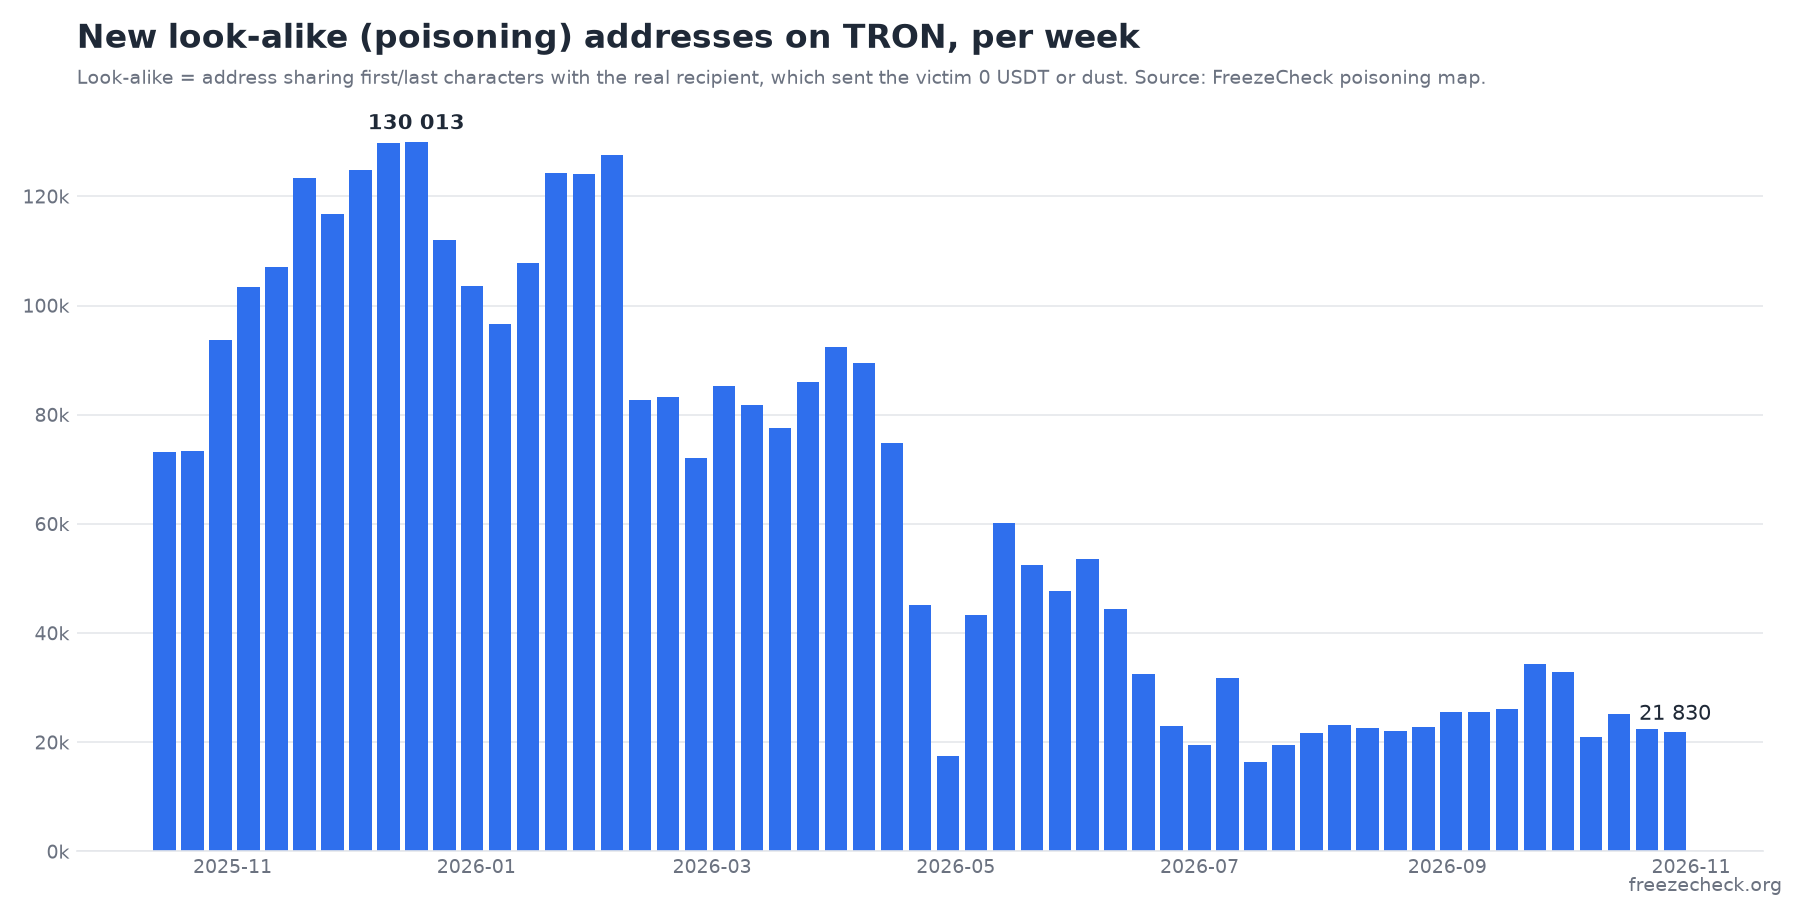
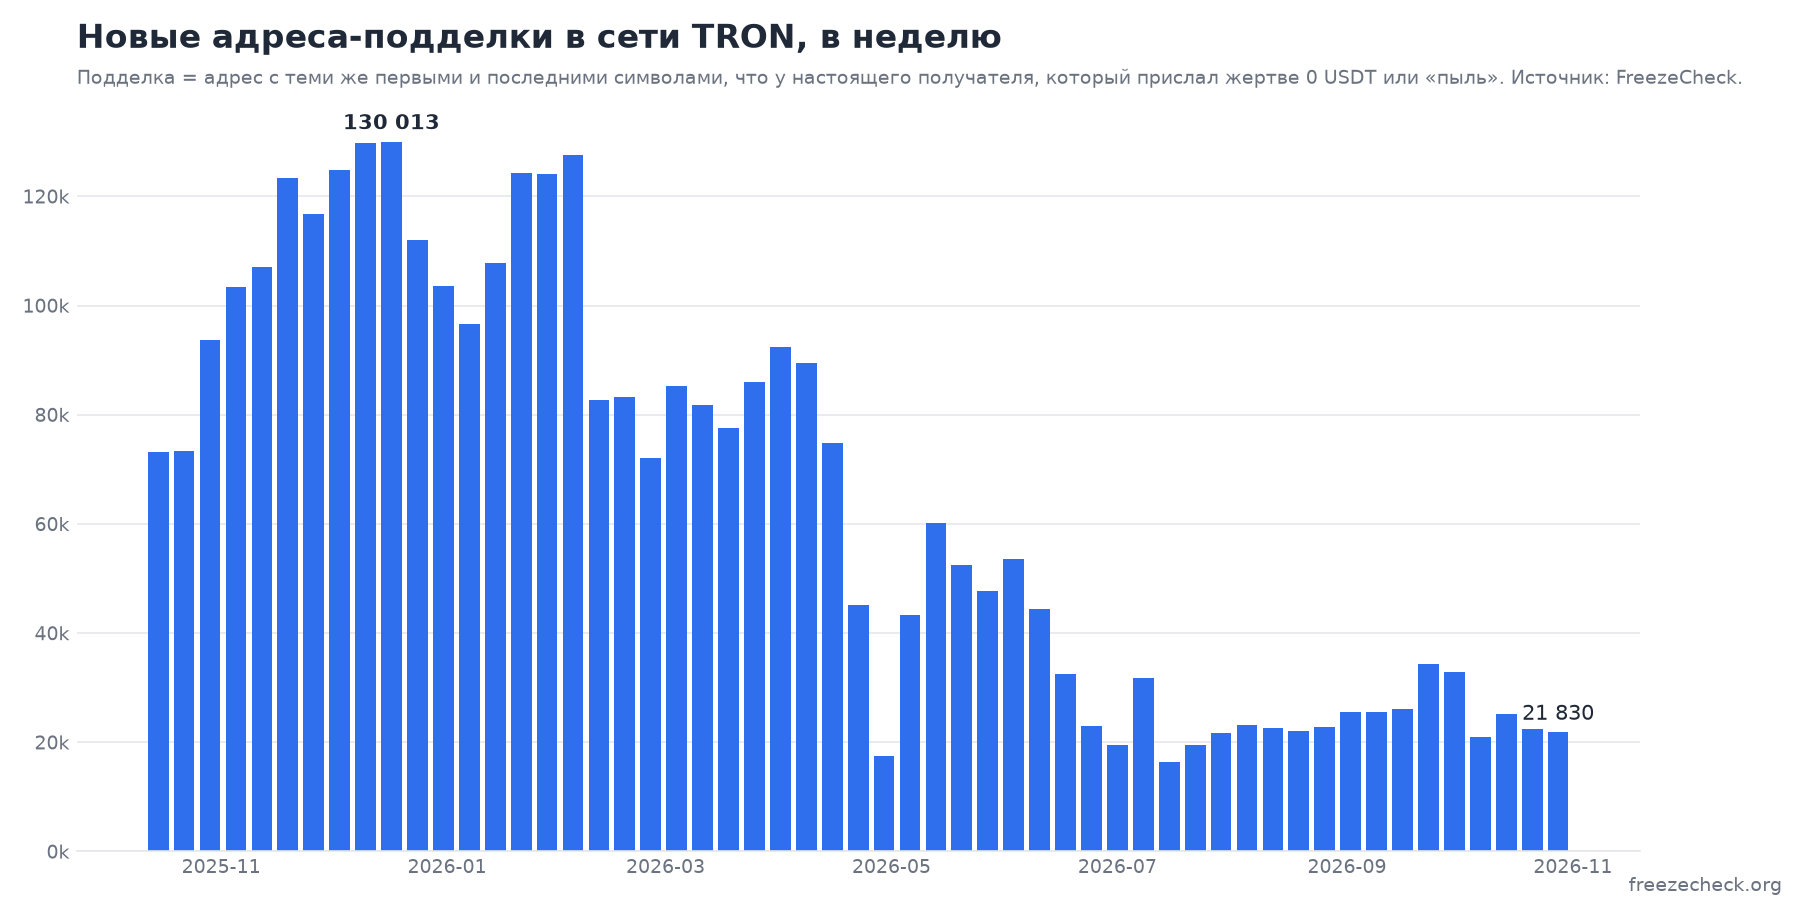
Address poisoning: 2.17M look-alike addresses on TRON in a year
55 weeks of data. Peak of 130,013 new fakes in one week in December 2025; about 3,000 a day now. 17 "factories"; only 27.5% of fakes carry a red tag on Tronscan.
Read the study →Downloads
Unfreezes and burns, CSV ↓All freezes with proposal times, CSV ↓Unfrozen theft addresses, CSV ↓Freeze share by group, CSV ↓Unnamed hot wallets, CSV ↓Poisoning by week, CSV ↓Full poisoning dataset, 7.3M addresses (Zenodo DOI) ↗
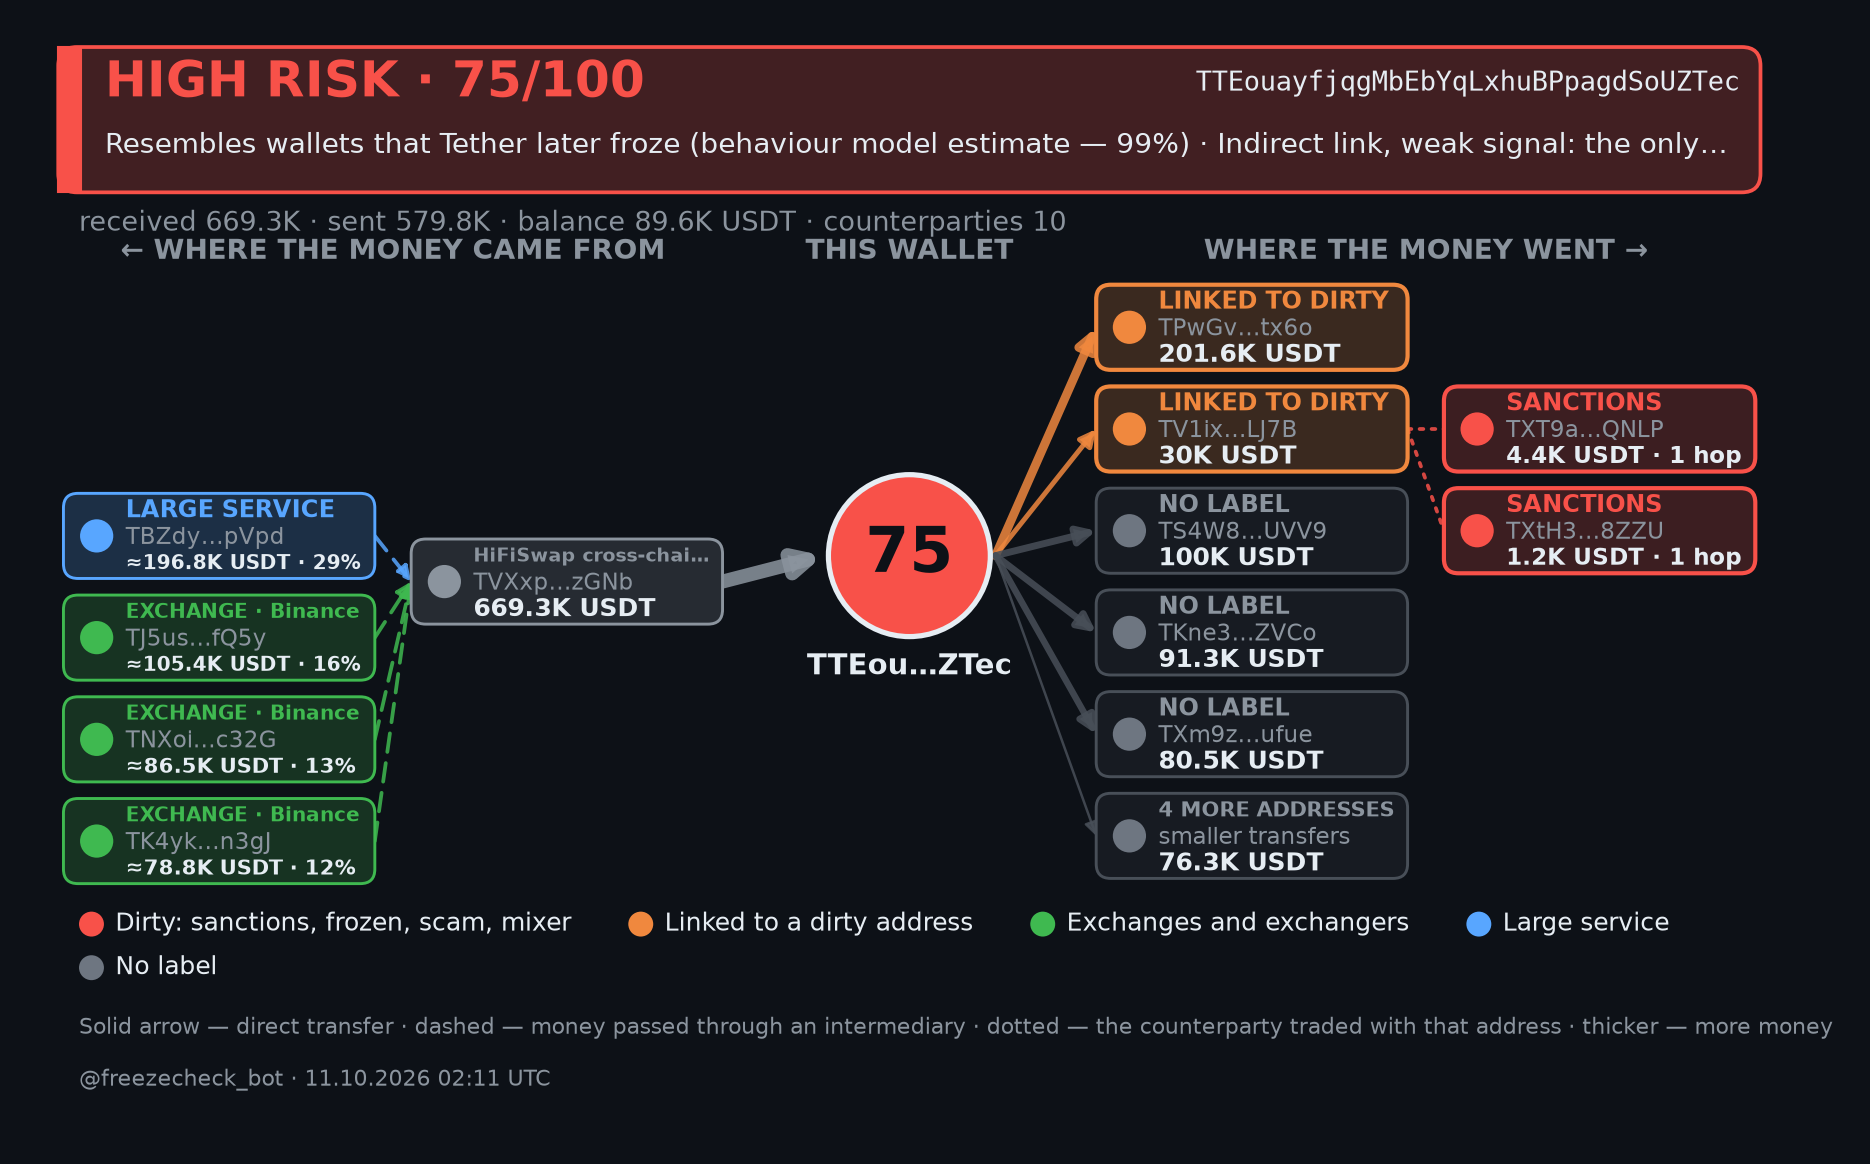
Chart: who Tether freezes, PNG ↓Chart: unnamed exchanges, PNG ↓Chart: poisoning, PNG ↓Sample report graph, PNG ↓
Russian versions of the charts: who Tether freezes, unnamed, poisoning.
How we measure
Raw data is the complete USDT TRC-20 transfer log, read from the public chain. Labels come from public sources (the Tether blacklist, OFAC, EU, UK and Israeli sanctions lists, US court records, Chainabuse, exchange proof-of-reserves) and from our own pattern detection: deposit sweeping for exchanges, look-alike prefixes and suffixes for poisoning, activation chains for fake factories.
Every figure in our studies comes with its time window and method, and is a lower bound unless stated otherwise. We do not name private individuals and do not claim intent; we describe what the transfers show.
What we can prepare
- Custom cuts of the data for a specific exchange, region, time window or sanctions case.
- A check of specific addresses from your investigation, with the trail of funds up to five hops.
- A comment from the team, in English or Russian, usually the same day.
- Early access to studies in progress: how much money leaves an address before Tether freezes it and where it goes; who is frozen and who is not.
Citing
Free to quote and republish charts with a credit: "Source: FreezeCheck (freezecheck.org)". A link to the study page is appreciated.
Fact sheet
- Product: a Telegram bot, @freezecheck_bot, launched in 2026. A mobile app is planned.
- Coverage: TRON network, USDT only. 65 million labelled addresses, updated daily.
- Accuracy: 84% of Tether freezes flagged in advance in a blind test on freezes the model never saw (93% after we tuned thresholds on the same freezes); 3% false alarms on random exchange clients.
- Public prediction log: verdicts recorded in advance and compared with new freezes every hour.
Contact
hello@freezecheck.org
Write with "Press" in the subject. We answer journalists first.